
Essential Eight Compliance & Maturity Assessment
Discover
Map goals, users, constraints, existing systems, and the business case before scope locks in.
Design
Shape the architecture, delivery plan, risk register, and success measures around your operating reality.
Build
Ship focused increments with working demos, testing, accessibility checks, and security review.
Support
Monitor, maintain, document, and improve the platform so your team can rely on it long term.
Nano Solutions assesses your Essential Eight maturity across all eight mitigation strategies, shows you exactly where you stand, builds a costed roadmap to your target level, and does the remediation — patching, application control, multi-factor authentication, hardening and backups. Established 2013, WA Government CUAICTS2021 panel supplier (Contractor #225). Assessment to compliant, with one team.
The ACSC Essential Eight is the baseline for Australian government and a fast-becoming standard for everyone who works with them. We don't just hand you a report — the same team that scores your maturity does the uplift work to close the gaps.
Who it's for
Essential Eight compliance matters most to:
- Government suppliers — organisations bidding for or holding WA and federal government contracts where an Essential Eight baseline is expected.
- WA mining & resources — operators and service providers protecting operational technology and corporate systems.
- Community-services organisations handling sensitive personal data.
- Any business that needs to prove its security baseline to win or keep contracts.
What is the Essential Eight?
The Essential Eight is ASD's baseline set of eight mitigation strategies for internet-connected corporate IT: patch applications, patch operating systems, multi-factor authentication, restrict administrative privileges, application control, restrict Microsoft Office macros, user application hardening, and regular backups. Maturity is scored per strategy from Level Zero to Level Three — and your overall level is your weakest strategy, not your average.
The full reference lives in our Essential Eight knowledge hub, where it stays current and sourced: a complete requirements matrix covering every strategy at every maturity level with the real patching timeframes, a page per strategy, and a tracker for where the framework is heading. This page is about the engagement: what we assess, what we fix, and what it costs.
One thing worth stating plainly, because it gets sold anyway: there is no such thing as Essential Eight certification. ASD's maturity model states there is no requirement for organisations to have their implementation certified by an independent party, and ASD does not endorse or register Essential Eight assessors. An independent assessment may still be required of you by a contract, a regulator or a government directive — that is a procurement obligation, not a certificate, and we will not pretend otherwise.
You can target a different maturity level per strategy. We help you set the right target based on your risk and obligations, then build a remediation roadmap with effort and risk reduction quantified.
Is the Essential Eight mandatory for my organisation?
It depends on who you are and who you work with:
- Non-corporate Commonwealth entities are directed to implement the Essential Eight — for them it is mandatory.
- WA Government agencies and their suppliers are increasingly required to demonstrate a defined maturity level, often Maturity Level Two, as a condition of contracts under arrangements such as the CUAICTS2021 ICT panel.
- Mining, resources and critical-infrastructure operators may fall under the Security of Critical Infrastructure (SOCI) Act, where the Essential Eight is a practical way to meet risk-management obligations.
- Everyone else — the Essential Eight is not law for private business generally, but it is the clearest, cheapest way to prove a security baseline to insurers, partners and prospects, and to reduce the risk that ends most small-business breaches.
If you are unsure which applies, that is exactly what the assessment answers: where you stand today, what level you actually need, and how to get there. Read our explainer on where the framework is heading for the wider context.
How we work
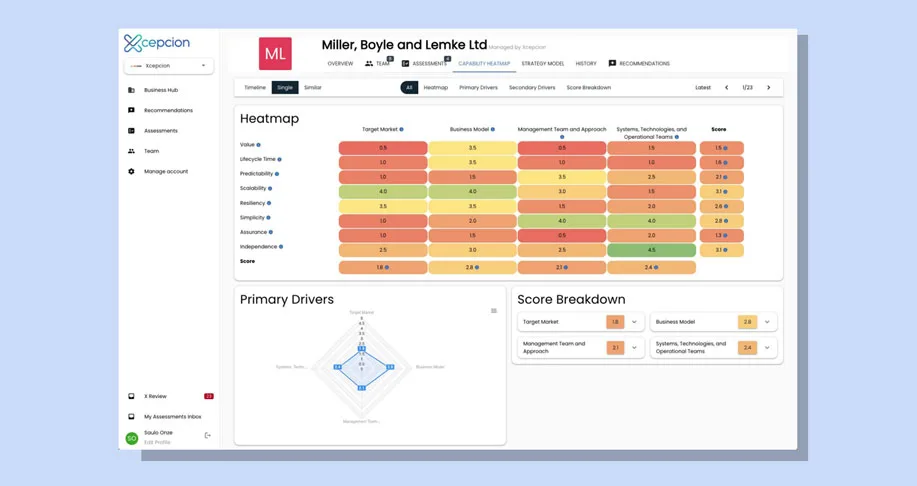
- Assessment (1–2 weeks, fixed) — evidence review and interviews produce a maturity scorecard across all eight strategies, plus a target-level gap analysis.
- Roadmap — a prioritised, costed uplift plan to your target maturity level, sequenced by risk reduction.
- Uplift (we do it) — patching, MFA rollout, application control, server hardening and a tested backup regime. We use automation tools like Ansible to keep systems hardened and consistent.
- Annual re-assessment retainer — maturity drifts as systems and people change; we keep you compliant and re-score on a cadence.
Where the Essential Eight is heading
On 15 October 2026 ASD published ASD Essentials, with chapters for enterprise IT, operational technology and cloud. ASD's FAQ describes it as replacing the Essential Eight. Maturity levels give way to priority phases, each action is rated not effective, partially effective or fully effective per domain, and ASD says Essential Eight maturity ratings "do not automatically translate" into the new ratings.
Worth being precise, because the reporting has not been: ASD has not set a retirement date for the Essential Eight. It says it will advise on transition timing "in due course", and that organisations should keep meeting any obligation that requires Essential Eight implementation or reporting. ASD also says every Essential Eight strategy maps to at least one ASD Essentials principle, and it does not recommend slowing or stopping uplift programs. The foundational controls (patching, MFA, admin restriction, application control and tested backups) carry forward.
If you already hold Essential Eight evidence, we can map it to ASD Essentials for enterprise IT and show where it carries forward and where it needs strengthening. Our dated Essentials transition tracker separates what ASD has published from what has only been reported.
Why Nano Solutions
We're a Fremantle-based custom software and cyber team — a WA Government CUAICTS2021 panel supplier (Contractor #225) — so we work with the exact organisations these obligations apply to, including government agencies. With 13 years running secure production systems for government and enterprise, Linux and server hardening is home turf. Critically, we advise, build, and run it: assessment, remediation and ongoing maintenance from one accountable team.
A note on scope
We provide Essential Eight assessment, roadmap and remediation services. Maturity ratings reflect the evidence reviewed at the time of assessment; maintaining a maturity level depends on your ongoing operations, which is what the re-assessment retainer is for.
Typical investment
- Essential Eight assessment: from $4,500 fixed — current-vs-target maturity scorecard across all eight strategies with a prioritised uplift plan.
- Uplift / remediation: scoped from the roadmap, based on the gaps found and your target maturity level.
- Annual re-assessment retainer: from ~$2,000/month — keeps your maturity from drifting and re-scores on a cadence.
Every engagement begins with a free 30-minute scoping call. Book an Essential Eight assessment and we'll tell you exactly where you stand — then close the gap.
Frequently Asked Questions
What is the Essential Eight?
The Essential Eight is the Australian Cyber Security Centre's set of eight baseline mitigation strategies that protect organisations against the most common cyber threats. The eight are: application control, patch applications, configure Microsoft Office macro settings, user application hardening, restrict administrative privileges, patch operating systems, multi-factor authentication, and regular backups. Maturity is measured across four levels (Maturity Level Zero through Three).
Who needs to comply with the Essential Eight?
Australian Government entities are directed to implement the Essential Eight, and — increasingly — so are their suppliers and any organisation that needs a defensible security baseline to win or keep contracts. For many WA Government and mining/resources contracts, achieving Maturity Level Two is becoming a practical requirement.
What maturity level do we need?
It depends on your risk profile and contractual obligations. Most organisations start by targeting Maturity Level One or Two; sensitive government and critical-infrastructure workloads target Level Three. We help you set the right target per strategy (they need not all be the same) and build the roadmap to reach it.
Can you remediate, not just assess?
Yes. We are a custom software and cyber team, not report-writers — the same team that scores your maturity does the patching, MFA rollout, application control, server hardening and backup work to close the gaps. Assessment to compliant, with one team.
How long does an Essential Eight assessment take?
Typically one to two weeks for the assessment and maturity scorecard across all eight strategies, including evidence review and interviews. Remediation timeframes depend on the gaps found and your target maturity level, and are costed in the roadmap.
Is the Essential Eight changing?
Yes. On 15 October 2026 ASD published ASD Essentials, which it describes as replacing the Essential Eight, with chapters for enterprise IT, operational technology and cloud. ASD has not set a retirement date and says it will advise on transition timing in due course, so the Essential Eight and its Maturity Model (levels 0–3) still apply wherever an obligation cites them. ASD says every Essential Eight strategy maps to at least one ASD Essentials principle, so existing work carries forward.
Have a question that's not listed here? We're happy to help.
Ask Us AnythingRelated Projects
Further Reading
- The Essential Eight is evolving: what ASD's new "Essentials" series means — what's proposed, what it means for Australian business, and what to do before it changes.
- Cybersecurity in Australia: key insights from FY2023-24 — the ASD threat report, an Essential Eight checklist, and critical-infrastructure protection.
- Secure code review — OWASP Top 10 and ASVS assessment of your application source code.
- Cloud maintenance & monitoring — 24/7 patching, monitoring and incident response to keep systems hardened and compliant.
Last reviewed: November 2026
Ready to Get Started?
Book a free discovery call to discuss your project. No obligation, no jargon — just a conversation about what you need.
